A major security breach at website testing
platform Optimizely exposed visitors to the websites of at least 178 major organizations
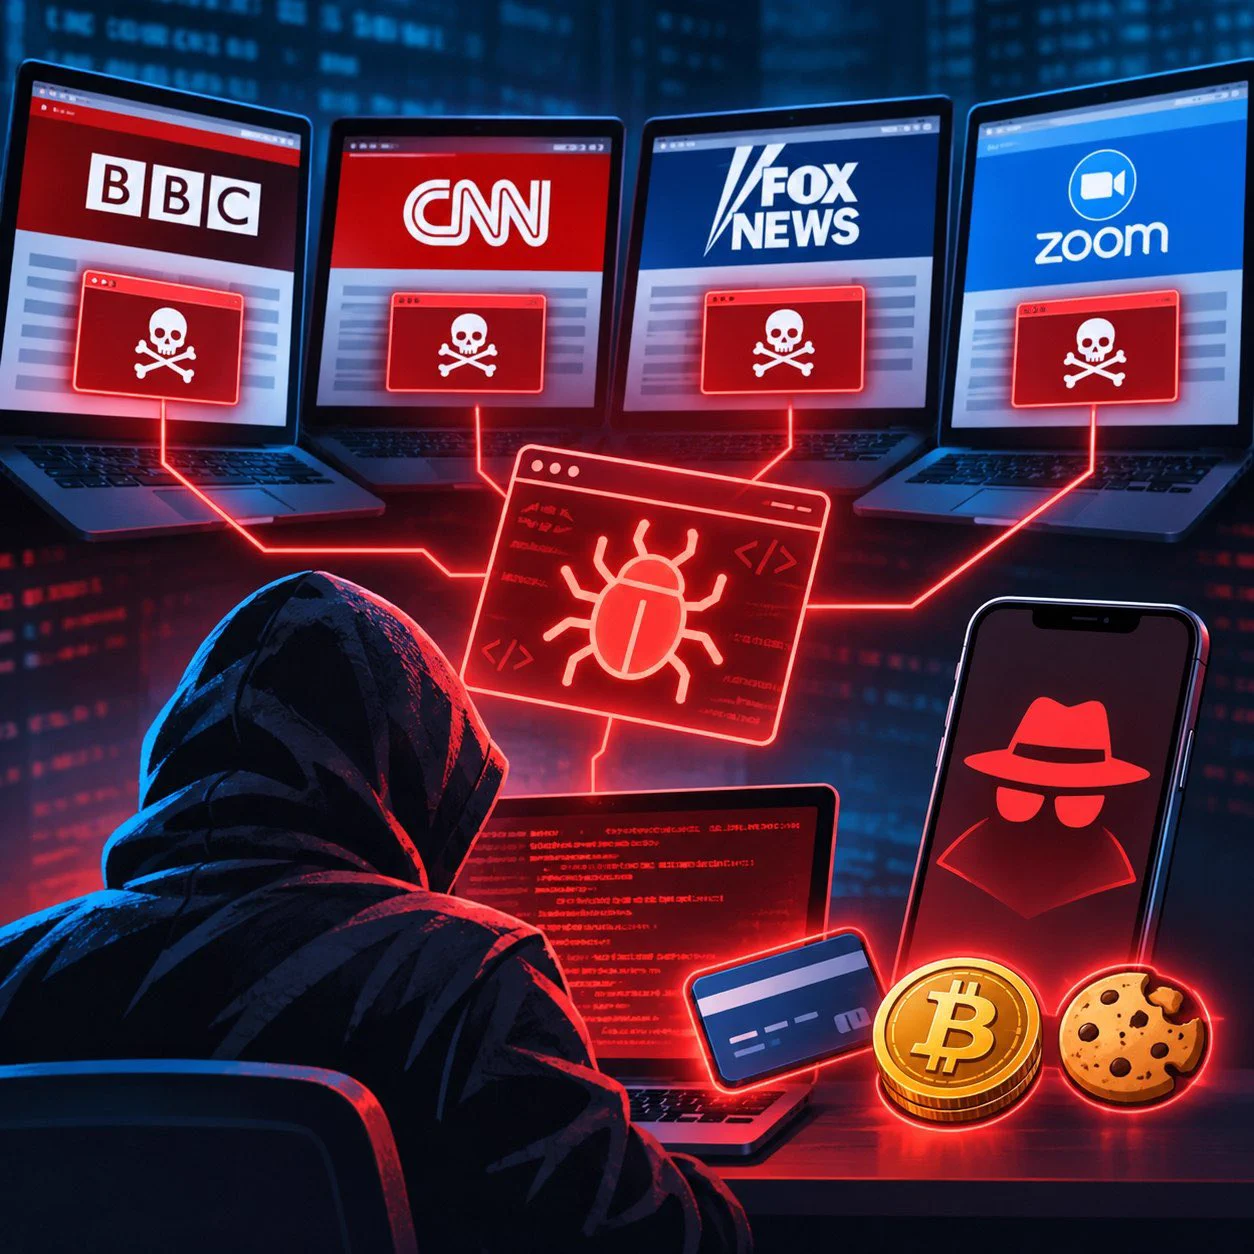
worldwide, including Zoom, BBC, CNN, Fox News, HSBC and IKEA, to dangerous
malware. According to cybersecurity firm Report URI, the attack was designed to
steal cryptocurrency payments and obtain sensitive data. During its
investigation, Report URI identified malicious code in 188 of Optimizely's
1,611 scripts. The firm believes the actual number of affected organisations
could be higher. The list of affected organizations also includes major names
such as Salesforce, GitLab, Equifax, Air France-KLM, Ledger and Peacock. The
earliest evidence of the attack was found in code delivered to BBC visitors at
11:21 p.m. Eastern Time on Sunday.
The malware functioned as a multipurpose toolkit.
During payment transactions, it replaced cryptocurrency wallet addresses with
those belonging to the attackers, redirecting payments into their wallets. By
2:25 p.m. on Monday, cryptocurrency transactions worth approximately $7,040 had
been confirmed in the attackers' wallets. In addition, the malicious code was
capable of stealing payment card details, browser cookies and screenshots. It
targeted older versions of iPhones and iPads, while collecting information from
devices running newer versions. According to cybersecurity experts, the
attackers had inserted their code into Optimizely's Project JavaScript feature.
Since the code was delivered through Optimizely's trusted domain, visitors to
affected websites became vulnerable even though the websites' own systems
remained secure. Optimizely has officially confirmed the security incident. The
company said an unauthorized party had exploited vulnerability in its platform
to inject malicious code into some of its customers' projects. The company said
it had fixed the vulnerability, removed the malicious code from affected
projects and introduced additional security measures to prevent similar attacks
in the future.